Indian Users Targeted by Sophisticated Blackmoon Banking Malware Disguised as Tax Alerts:
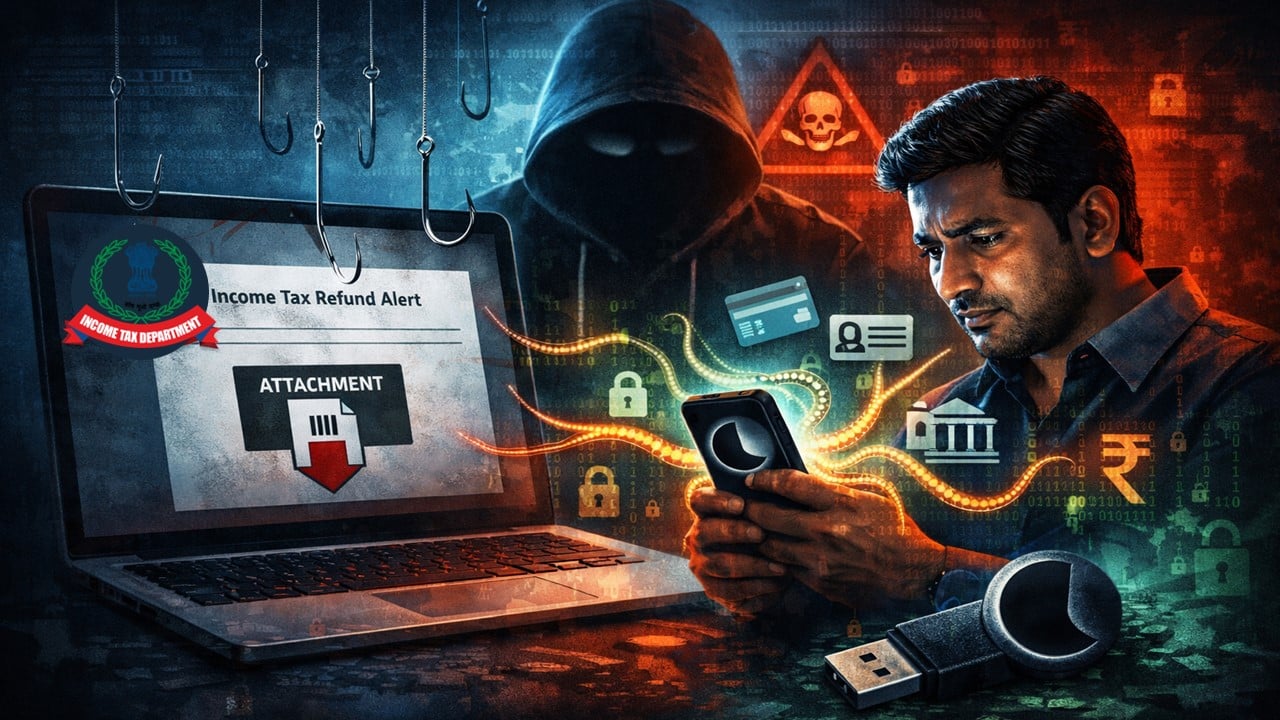
Indian users are being targeted by phishing emails posing as Income Tax alerts, tricking them into downloading Blackmoon malware that secretly steals sensitive banking and personal data.
Fake Tax Alerts Spread Blackmoon Malware
 Saloni Kumari
 Jan 27, 2026

Indian Users Targeted by Sophisticated Blackmoon Banking Malware Disguised as Tax Alerts
Nowadays, Indian users are being targeted in a phishing attack where hackers send fake messages or emails to trick people into clicking on malicious links. Once clicked, a hidden backdoor is installed on the victim’s device, allowing attackers to secretly access data. This attack is believed to be part of a cyber-espionage campaign aimed at spying on sensitive information, as per a report published by The Hacker News.
According to the report, the phishing messages include a ZIP file. When this file is opened and downloaded by someone, it begins a step-by-step malware attack. The key objective of this attack is to make the user download a banking virus called Blackmoon (also known as KRBanker). To hide malicious activity, this file also makes users install a real business security tool called SyncFuture TSM (Terminal Security Management), developed by a Chinese firm named Nanjing Zhongke Huasai Technology Co., Ltd.
The said activity has been identified by the cybersecurity researchers from the eSentire Threat Response Unit (TRU). Using this scam, the accused allegedly sent bogus emails acting to belong to India’s Income Tax Department. These emails made users afraid of the tax penalties imposed on them, creating urgency and fear, tricking them into quickly opening harmful attachments that can infect their devices or steal information.
In reference to the report, eSentire said, "By deploying this system as their final payload, the threat actors establish resilient persistence and gain a rich feature set to monitor victim activity and centrally manage the theft of sensitive information." Also said, "It provides them with the tools to not only steal data but to maintain granular control over the compromised environment, monitor user activity in real time, and ensure their own persistence."
Further stated, "By blending anti‑analysis, privilege escalation, DLL sideloading, commercial‑tool repurposing, and security‑software evasion, the threat actor demonstrates both capability and intent."
About Author


Saloni Kumari
Content Writer
Saloni is a Content Writer with 2+ years of experience at studycafe.in. She writes legal, taxation, and finance related content including GST, Income Tax etc. Skilled in translating complex judicial pronouncements and regulatory developments into clear, and reader-friendly articles. Experienced in covering judgements of ITAT, High Court, GSTAT, and news related to Income Tax, GST, and corporate law. She can be reached at [email protected].
Saloni is a Content Writer with 2+ years of experience at studycafe.in. She writes legal, taxation, and finance related content including GST, Income Tax etc. Skilled in translating complex judicial pronouncements and regulatory developments into clear, and reader-friendly articles. Experienced in covering judgements of ITAT, High Court, GSTAT, and news related to Income Tax, GST, and corporate law. She can be reached at [email protected].
 StudyCafe
 Delhi, Delhi, India
 2880
My Recent Articles
- ITAT Deletes Rs 2.67 Crore Section 68 Addition, Rejects Retrospective Source-of-Source Requirement
- RBI Eases Foreign Exchange Compliance for Small Exporters and Freelancers
- GST Council Proposes Major Reforms in Registration, ITC, Refunds and Arrest Rules
- Govt Fixes 7.1% Interest Rate on Special Deposit Scheme for Non-Government PF Funds From Oct to Dec 2026
- CBI Apprehends Principal of Eklavya Model Residential School, Nuapada, for Demanding Rs 20,000 Bribe
Up Next
Loading suggestions…


Recent Posts
All Posts
Tags
Recent Posts
All Posts